RD / Training

Learn to find vulnerabilities in code, prove them and get them fixed.

One-to-one online training in secure code review and code-assisted web and API penetration testing, taught in English, or in Arabic for Arabic speakers. I teach every student personally and adapt the pace, exercises and depth to what you already know. The material comes from my own work: I have reported 150+ security vulnerabilities and wrote the patches for two Linux kernel CVEs.

One-to-one · Online · Taught in English, or Arabic for Arabic speakers · Intermediate level

Each course is a complete one-to-one programme for $1,490: about 15 hours of live sessions, labs, review of your exercises and a final assessment. Your first 20-minute assessment call is free, and we agree your plan and start date after it.

01Training

Two courses, taught one to one

Each course has a full syllabus. Your plan starts from a short assessment of what you already know, so your time goes where you need it, at your pace.

01

Secure code review

Learn to read an unfamiliar codebase the way an attacker would: trace untrusted input to the line that breaks, prove the vulnerability is exploitable and write a fix developers accept. Taught one to one, online, at your pace.

Level
Intermediate
Format
One-to-one live online sessions, with labs between sessions
Pace
Set for you after an initial assessment

$1,490 per course

See the syllabus
02

Web & API penetration testing

Learn to run a web and API penetration test the way a professional engagement runs: scope it, test it with the source code open, prove the impact safely, report it and verify the fix. Taught one to one, online, at your pace.

Level
Intermediate
Format
One-to-one live online sessions, with labs between sessions
Pace
Set for you after an initial assessment

$1,490 per course

See the syllabus
03

Training for your engineers

Sponsor individual training for one or more developers or security engineers. Each person is taught one to one, online, with a plan built around their level and the languages and frameworks your team uses.

Format
One-to-one online training for each engineer
For
Developers, application security and security engineers
Courses
Secure code review, or web and API penetration testing

$1,890 per engineer

How it works

02Prices

Clear prices for one-to-one training

Each course is a complete programme: about 10 live one-to-one sessions of 90 minutes, labs prepared for the course, review of your exercises between sessions, a final assessment and a certificate of completion. The first 20-minute assessment call is free.

Secure code review course

$1,490per course

Read code like an attacker, prove what you find and get it fixed.

Web application penetration testing course

$1,490per course

Test web apps and APIs with the source open, from scope to retest.

Both courses

$2,690for both courses

One plan from source code to the running application, $290 less than the two courses separately.

Training for your engineers

$1,890per engineer

The same one-to-one programme for each engineer your company sponsors.

Single session

$150per session

90 minutes one to one on a question you choose: a finding you are stuck on, a review of your own code or the next step in your learning.

Prices are in US dollars. Your plan, number of sessions and start date are agreed after the free assessment call.

03Why one-to-one

Taught to you, from real vulnerabilities.

Shaped around your level

We start with a short assessment. I then set the order, pace and depth of the material for you, move quickly through what you already know and spend longer where you need it.

Cases from vulnerabilities I analysed

Modules are built around real code, including CVE write-ups I published, such as the fast-jwt fix that took three attempts, and the two Linux kernel CVEs I fixed. You trace each flaw in source, then confirm it on a running copy of the application on your machine.

Your work, reviewed by me

I review your exercises and your final report myself and go through them with you in our sessions.

In English, or in Arabic

Sessions are taught in English for international students, and in Arabic for Arabic speakers who prefer it. Arabic sessions keep the English terms you will meet in tools, reports and job descriptions.

04Instructor

Taught by Rand Deeb

I am an application security engineer and an independent security researcher. I prepare the material, labs and exercises myself and supervise every student personally.

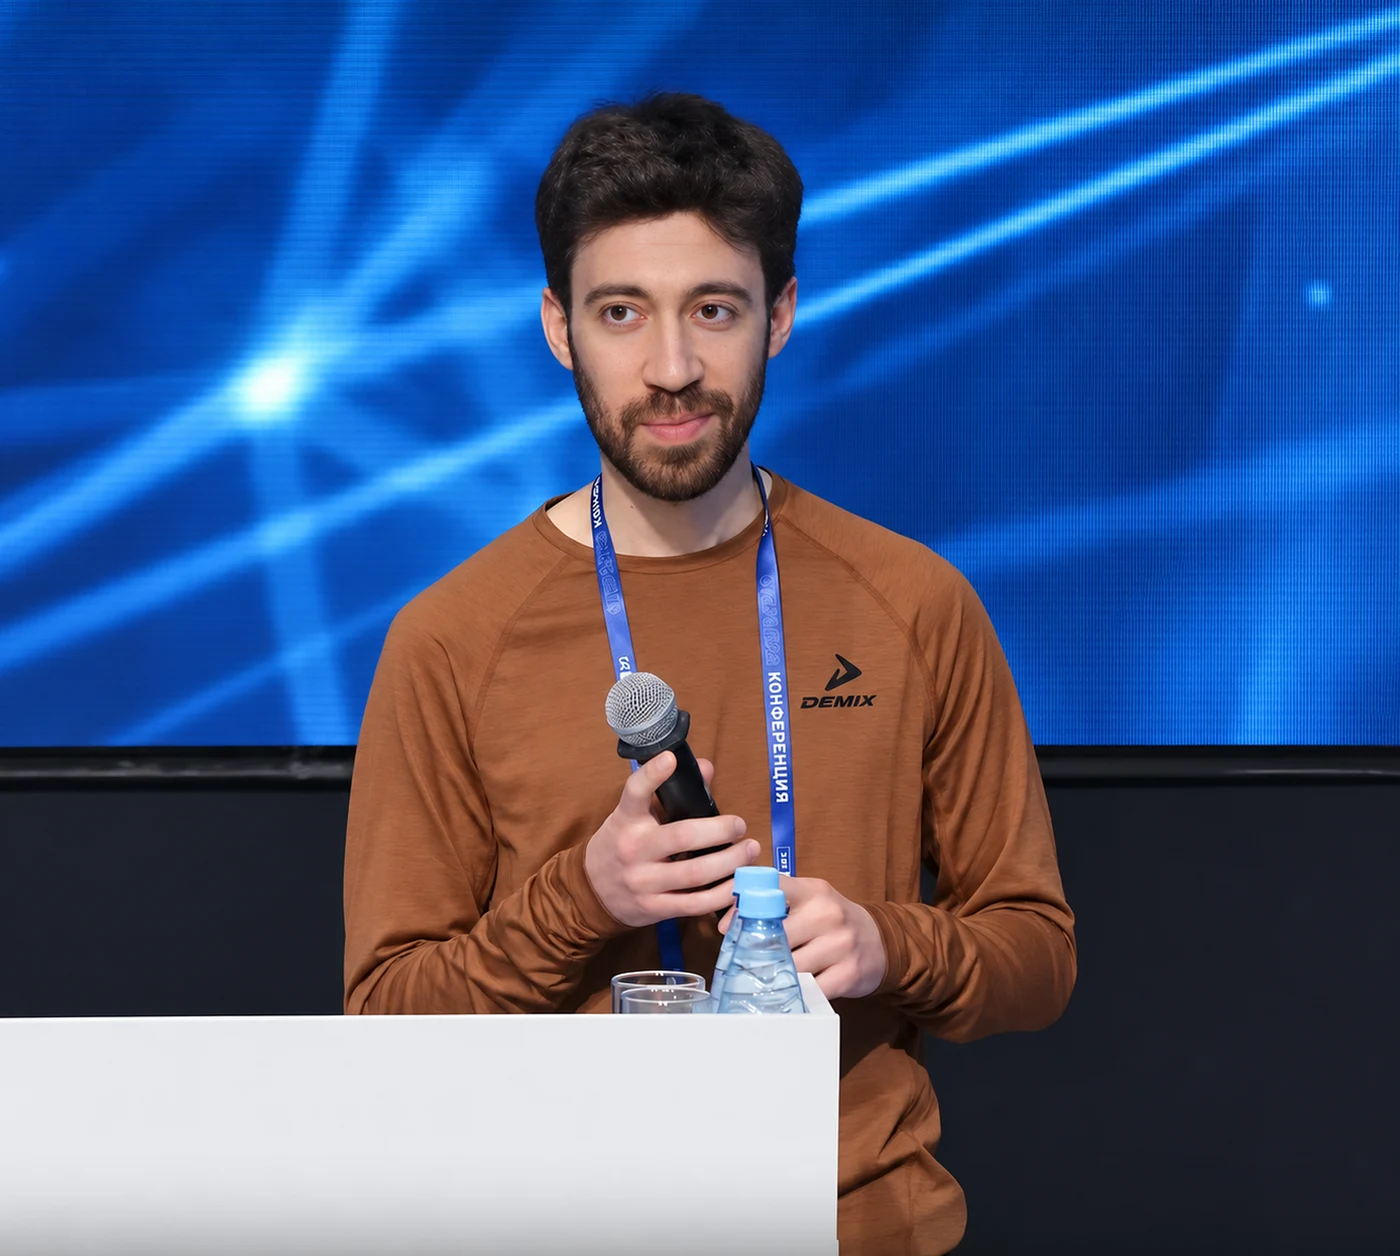
Rand Deeb speaking at ISP RAS Open 2024 in Moscow, holding a microphone in front of a blue conference screen
  • 150+ security vulnerabilities reported, including seven in Facebook and Instagram that Meta validated and acknowledged.
  • Two Linux kernel CVEs, CVE-2024-26855 and CVE-2025-37858, fixed with my own patches; nine patches merged into mainline Linux.
  • More than 300 static-analysis reports triaged in Linux kernel code: the daily skill of separating real findings from tool noise.
  • Lead application security engineer, working on SAST, DAST and C++ security engineering.
  • Speaker at ISP RAS Open 2024 in Moscow.

05Learning path

Where to start

  1. 01

    Read code like an attacker

    Secure code review: trust boundaries, data flow, authentication, authorization and business logic, from source to proof to fix.

  2. 02

    Test like a professional

    Code-assisted web and API penetration testing: scoping, testing, reporting and retesting a realistic engagement.

  3. 03

    Train your engineers

    Company-sponsored one-to-one training for one or more developers or security engineers, each with their own plan.

06Start today

Read how I traced real vulnerabilities

These free write-ups use the same method the courses teach. Each one follows a vulnerability from its source to its fix.

07Questions

Questions

When can I start?

Send a short message about your level and goals. I reply within three days to arrange a free 20-minute assessment call, and we agree your plan and start date after it.

How much does it cost?

Each course costs $1,490 for about 10 one-to-one sessions of 90 minutes, with labs, exercise review, a final assessment and a certificate. Both courses together cost $2,690, and a single 90-minute session costs $150.

How does one-to-one training work?

We meet online for live sessions. Between sessions you work on labs and exercises I set for your level, and in the next session we go through your results. The pace follows your progress, not a fixed timetable.

Which course should I take first?

If you can read code and know the common web vulnerability classes, start with secure code review. If you already test web applications and want a professional, code-assisted method, start with the penetration testing course. Both are intermediate; I suggest a starting point after a short assessment of your level.

Which language are the sessions in?

English for international students. Arabic speakers can choose Arabic or English; Arabic sessions keep the English terms you will see in tools, reports and job listings.

Is any of the training in person?

No. All sessions, labs, exercises and feedback are online.

Will I receive a certificate?

You receive a certificate of completion when you pass the final assessment. It is issued by me and is not an industry certification such as OSWE. What an employer can check is the work itself: your final report.

Are the hands-on exercises legal?

Yes. All practical work uses applications I prepared for the course and open-source projects at versions with published advisories, running on your own machine. You never test a system you do not own or have written permission to test.

What if I need more time?

If you need more sessions than planned, each extra session costs $150, and we agree it before it happens.

Can my employer pay?

Yes. Mention it in your message, or see the page on training for companies.

08Contact

Ready to start?

Send a short message: which course, Arabic or English, your current level and what you want to be able to do. I reply within three days to arrange your free assessment call.