
Rand Deeb
I find vulnerabilities, and I write the fixes.
I’m Rand Deeb, a lead application security engineer and independent security researcher. I have reported 150+ security vulnerabilities, wrote the fixes for two Linux kernel CVEs and built the Hendra DAST scanner. I test web apps and APIs for product teams and do the work myself.
Software engineering meets information-security research.
I hold a bachelor’s degree in Software Engineering and have completed doctoral studies (aspirantura) in Information Security in Russia. I passed the university defense; the final dissertation defense is pending. This background connects how systems are designed and built with research into how they can fail. I apply both perspectives to architecture, vulnerability discovery and remediation.
My full-stack development background helps me understand how a feature is built and how a fix will affect the rest of the application. I combine that perspective with security testing, code review and vulnerability research.
I also design and develop security applications for static analysis (SAST) and dynamic testing (DAST). This work connects software architecture, detection logic and reproducible evaluation, experience I can apply to a scoped tool development or extension project.
At Confident, my engineering work spans SAST, DAST, C++ and security engineering. Previously, I worked in web development and web security at Momento.
Meta has validated and acknowledged seven security vulnerabilities I reported in Facebook and Instagram. In Linux kernel code, I have triaged more than 300 static-analysis reports and contributed nine patches. My work also includes two published CVEs, CVE-2024-26855 and CVE-2025-37858, with fixes accepted into mainline Linux. The ice driver fix was backported to stable trees. The CVE records and linked fixes are available for you to inspect.
Hendra is a concrete example: a modular, context-aware DAST scanner I developed during my completed doctoral research project at ITMO University. I designed its core architecture and the components for technology identification, scan planning, request deduplication, finding review and benchmarking. My publications examine the methods behind this work.
If you are preparing a release or answering a customer’s security review, send me a short brief.
01Expertise you can verify
Proof you can check yourself
Numbers from my security work, with links to the public records behind them.
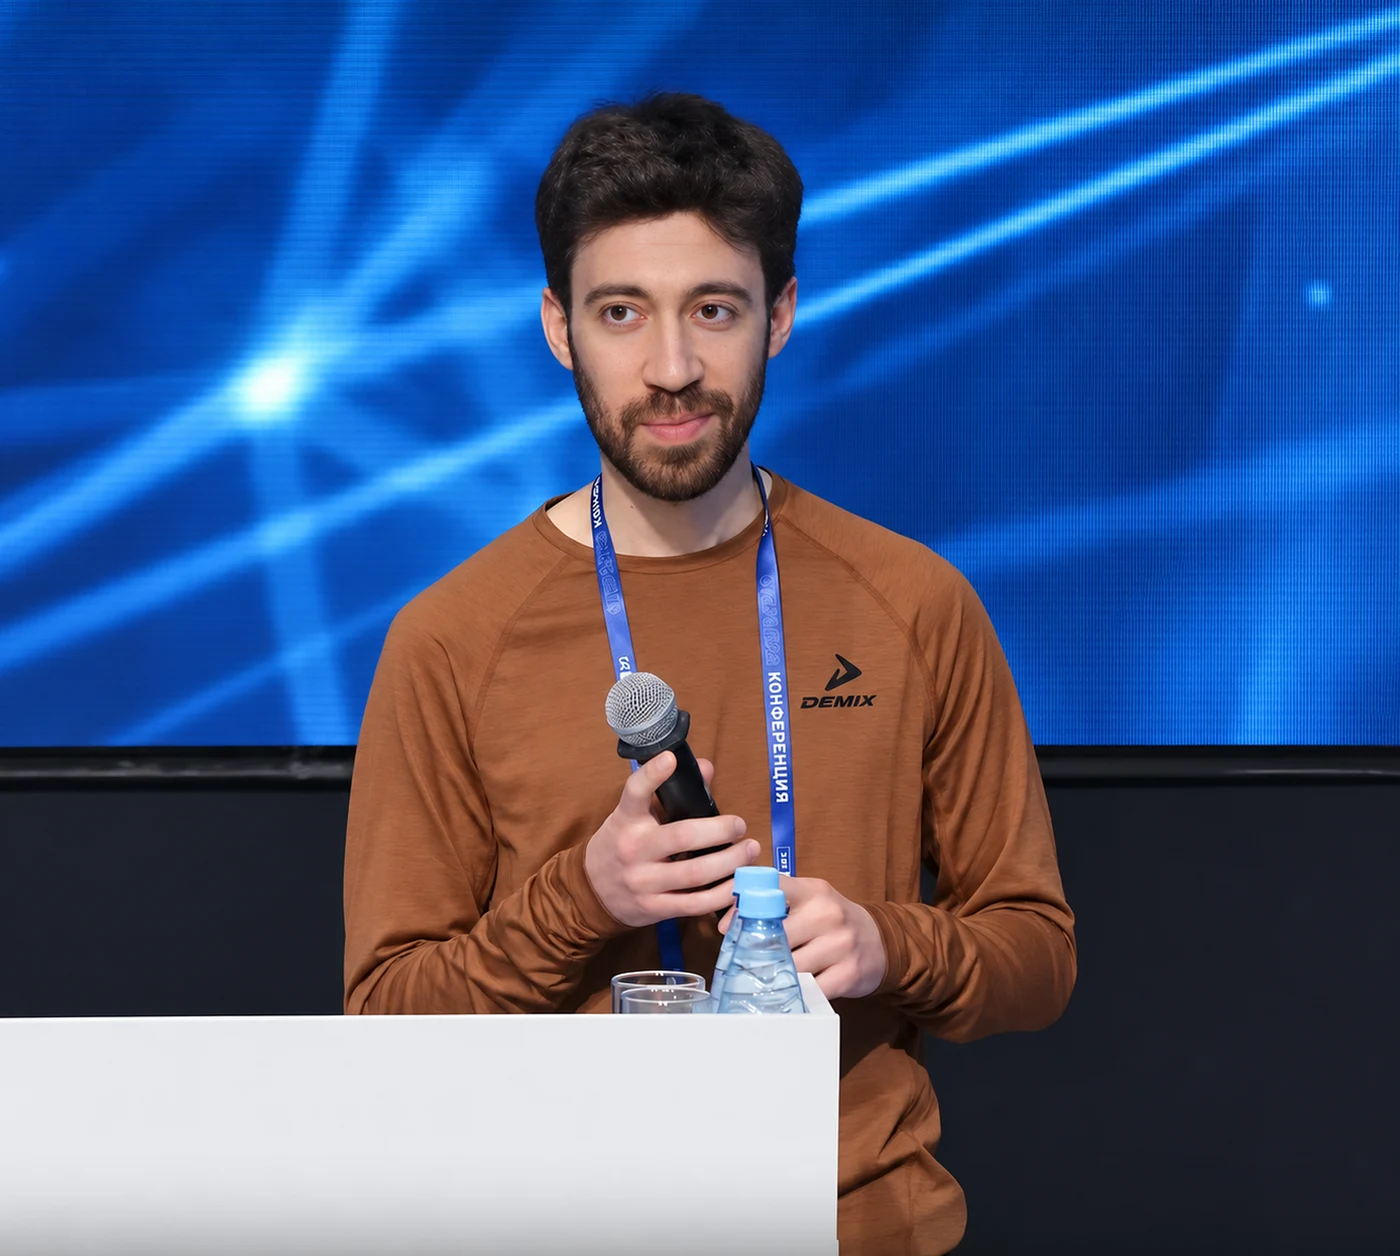
Conference speaker · ISP RAS Open 2024
Research presented in Moscow.
At ISP RAS Open 2024, I presented my research on using machine learning to predict web-stack technologies beyond traditional fingerprints. My talk is listed in the official conference programme.
Predicting web-stack technologies with machine learning: beyond traditional fingerprints
A practical question behind application testing: what is the software actually built with?
View the conference programme05About
Engineering & security experience
Lead Application Security Engineer
Confident · ООО «Конфидент»
Secure code review, vulnerability validation and security engineering across SAST, DAST, C++ and SIEM.
Independent security researcher
Meta Bug Bounty · Bugcrowd
Web development & web security manager
Momento
Bachelor’s project on SAST · Master’s on DAST · Completed doctoral research at ITMO University
ITMO University
08Contact
Shipping something that handles user data?
Send me a short brief. I reply within three days with questions or a proposal outline, and the price is agreed in writing before work starts.